22 posts tagged with "CTF"

View All Tags

SECCON CTF 14 Finals 作問感想

· 20 min read

2/28〜3/1の2日間、SECCON CTF 14の本戦が行われました!

参加した皆さんありがとうございます & 入賞したみなさんおめでとうございます 🎉
今年は、1日目がJeopardyで2日目がKing of the Hillという競技形式でした。両日でまったく異なる競技形式であるため、1〜2日目の間の夜に寝る間も惜しんで問題に挑む今までの慣習(いわゆる宿題)がなかったのは参加者視点だと大きかったかと思います。

私はJeopardyのweb問とjail問を作問しました。Slay the Noteは特におすすめです!

ChallengeCategoryIntended
Difficulty
Solved / 9
(Internatinal)
Solved / 9
(Domestic)
Keywords
Warmupwebwarmup99stream
DOMDOMDOMPurifywebeasy99DOMPurify, mXSS
Shadow CSSwebmedium10Firefox, Link
Slay the Notewebmedium00cookie parser
increasingjailmedium44pyjail

各問題のソースコードやソルバはリポジトリにpush済みです:

※ この記事はwriteupではなくて作問の背景や感想です。
Cross-Site ETag Length Leak

· 14 min read

I recently discovered a new client-side attack technique that leaks the length of an ETag from a cross-site page. This can be used as an XS-Leak oracle and I created a CTF challenge as a proof of concept.

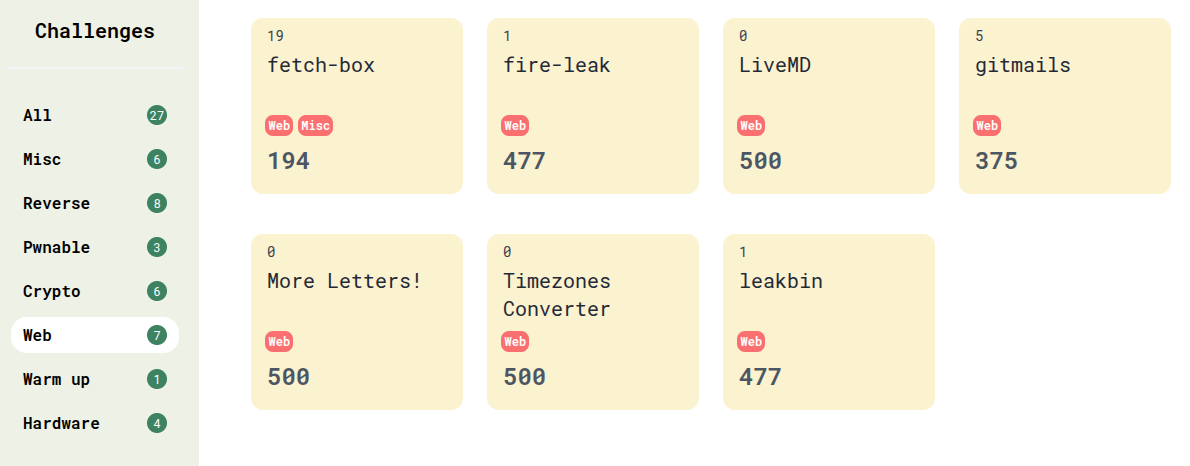
impossible-leak is one of the challenges I authored for SECCON CTF 14 Quals1:

This technique is likely applicable beyond this specific challenge. We can use it as an unintended solution in other XS-Leak challenges. In fact, I first came up with it as an unintended approach during an earlier CTF and later refined it into a standalone technique.

Footnotes​

  1. The full list of my SECCON CTF 14 Quals challenges is available here. ↩

  2. Here is parrot's solution for this challenge. It is unintended, but incredibly clever! ↩

Forcing Quirks Mode with PHP Warnings + CSS Exfiltration without Network Requests

· 9 min read

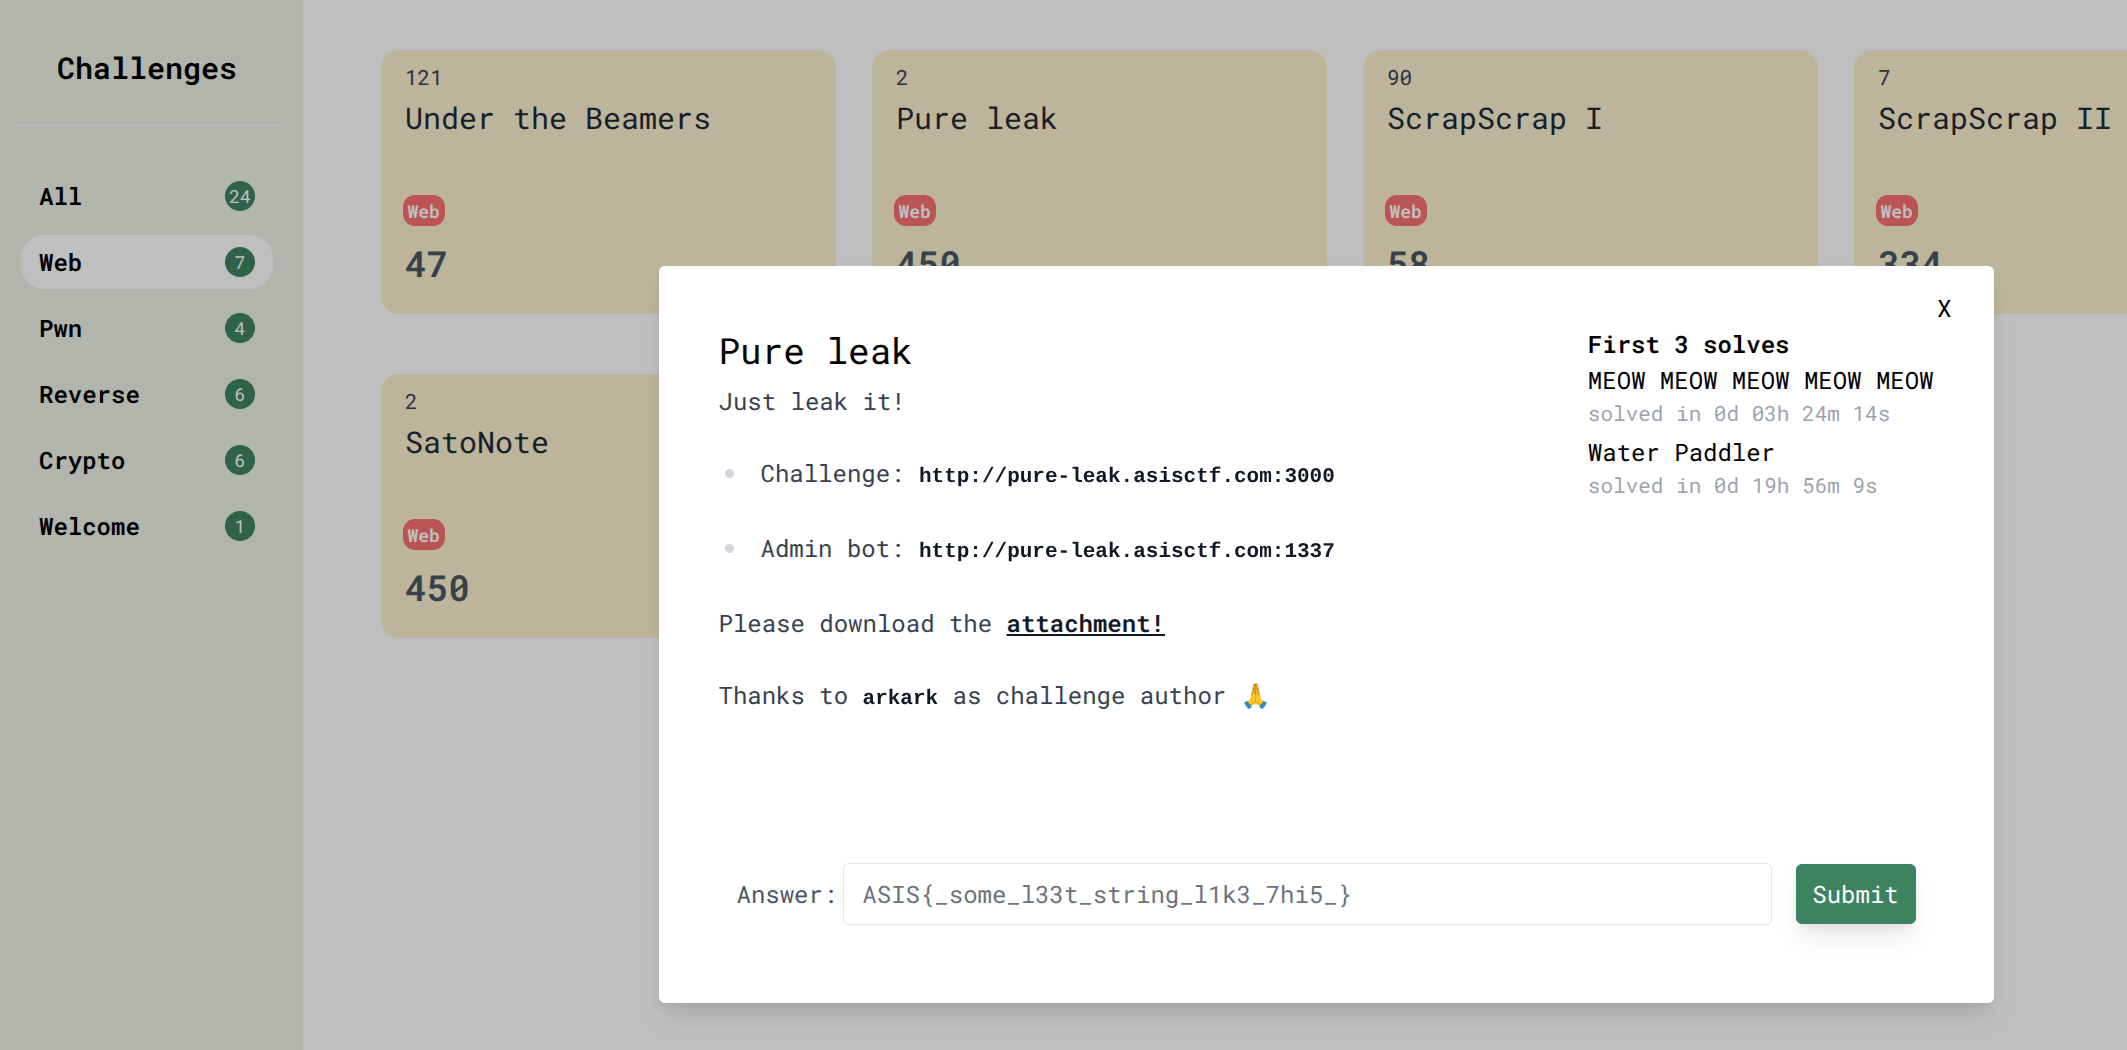
I made a web challenge pure-leak for ASIS CTF Quals 2025 as a guest author.

Congrats to MEOW MEOW MEOW MEOW MEOW and Water Paddler for solving it! 🎉

Despite its simplicity, the solution relies on several neat HTML/CSS tricks. Below I'll outline the key ideas and how they fit together.

AlpacaHack Round 7 (Web) - 作問者writeup

· 8 min read

AlpacaHackは個人戦のCTFを継続して開催する新しいCTFプラットフォームです。今回はst98さんと一緒にWeb回であるRound 7の作問を、担当しました。ご参加いただいた方々、ありがとうございました。

AlpacaHackにはwriteupを投稿する機能があるので、ぜひwriteupを書いて投稿してみてください。upsolveもOKです。AlpacaHackは常設CTFでもあるので、終わったCTFも実際にリモート環境でテストすることが可能です!

さて、今回は以下の問題をつくりました。本記事はそのwriteupになります。

ChallengeCategoryKeywordsSolved
Treasure HuntwebURL encoding71
minimal-wafwebXSS4
disconnectionwebbrowser behavior5
disconnection-revengewebbrowser behavior1

AlpacaHack Round 2 (Web) - 作問者writeup

· 21 min read

AlpacaHackは個人戦のCTFを継続して開催する新しいCTFプラットフォームです。keymoonとminaminaoが中心メンバーとなって動いており、最近リリースされました🎉

今回はWeb回であるRound 2の作問を担当しました。ご参加いただいた方々、ありがとうございました。参加登録した人数を数えると300!?ありがたすぎる...1

AlpacaHackにはwriteupを投稿する機能があるので、ぜひwriteupを書いて投稿してみてください。upsolveもOKです2。また、今後の作問・運営のためにもGoogleフォームでのfeedbackをいただけると非常に助かります。単純にモチベーションにもつながります。SNS上での感想も大歓迎です。

さて、今回は以下の問題をつくりました。本記事はそのwriteupになります。

ChallengeCategoryKeywords (spoiler)Solved
Simple LoginwebSQL injection84
Pico Note 1webCSP bypass, JavaScript10
CaaSwebRCE, Perl13
Pico Note 2webImport Maps3

Footnotes​

  1. 加えて、あまり広くリーチできていなかったというのと、タイムゾーンの問題があったにもかかわらず、海外の強い方にも多く参加してもらえてびっくり&感謝です。CTFTimeに登録したのも一定以上の効果があったりする? ↩

  2. AlpacaHackは常設CTFでもあるので、終わったCTFも実際にリモート環境でテストすることが可能です! ↩

SECCON CTF 2023 Finals: Author Writeups

· 17 min read

I wrote 4 web challenges and 1 misc challenge for SECCON CTF 2023 Finals. I hope you enjoyed the CTF and want to read your feedback and writeups.

My challenges:

ChallengeCategoryIntended
Difficulty
Solved / 12
(Internatinal)
Solved / 12
(Domestic)
Keywords
babywafwebwarmup84WAF bypass
cgi-2023webmedium52XS-Leak, SRI
LemonMDwebmedium21Islands Architecture
DOMLeakifywebhard10CSSi on style attributes
whitespace.jsmisceasy22JavaScript sandbox

I added the source code and author's solvers to my-ctf-challenges repository.

SECCON CTF 2023 Quals: Author Writeups

· 21 min read

Thank you for playing SECCON CTF 2023 Quals! I created some challenges for this CTF, just like 2021 and 2022. I hope you had fun and I'm looking forward to reading your writeups.

My challenges:

ChallengeCategoryIntended
Difficulty
KeywordsSolved / 653
blinkwebeasyDOM clobbering14
eeeeejswebmediumejs, XSS puzzle12
hidden-notewebhardXS-Leak, unstable sort1
craboxsandboxwarmupRust sandbox53
node-ppjailsandboxmediumprototype pollution5
deno-ppjailsandboxhardprototype pollution2

I added the source code and author's solvers to my-ctf-challenges repository.

zer0pts CTF 2023 writeup (4 web challs)

· 22 min read

zer0pts CTF 2023 に./Vespiaryで参加して8位でした!

guess要素が一切なく、各問題もよく構成されたものが多く、例年通りとてもたのしいCTFでした。